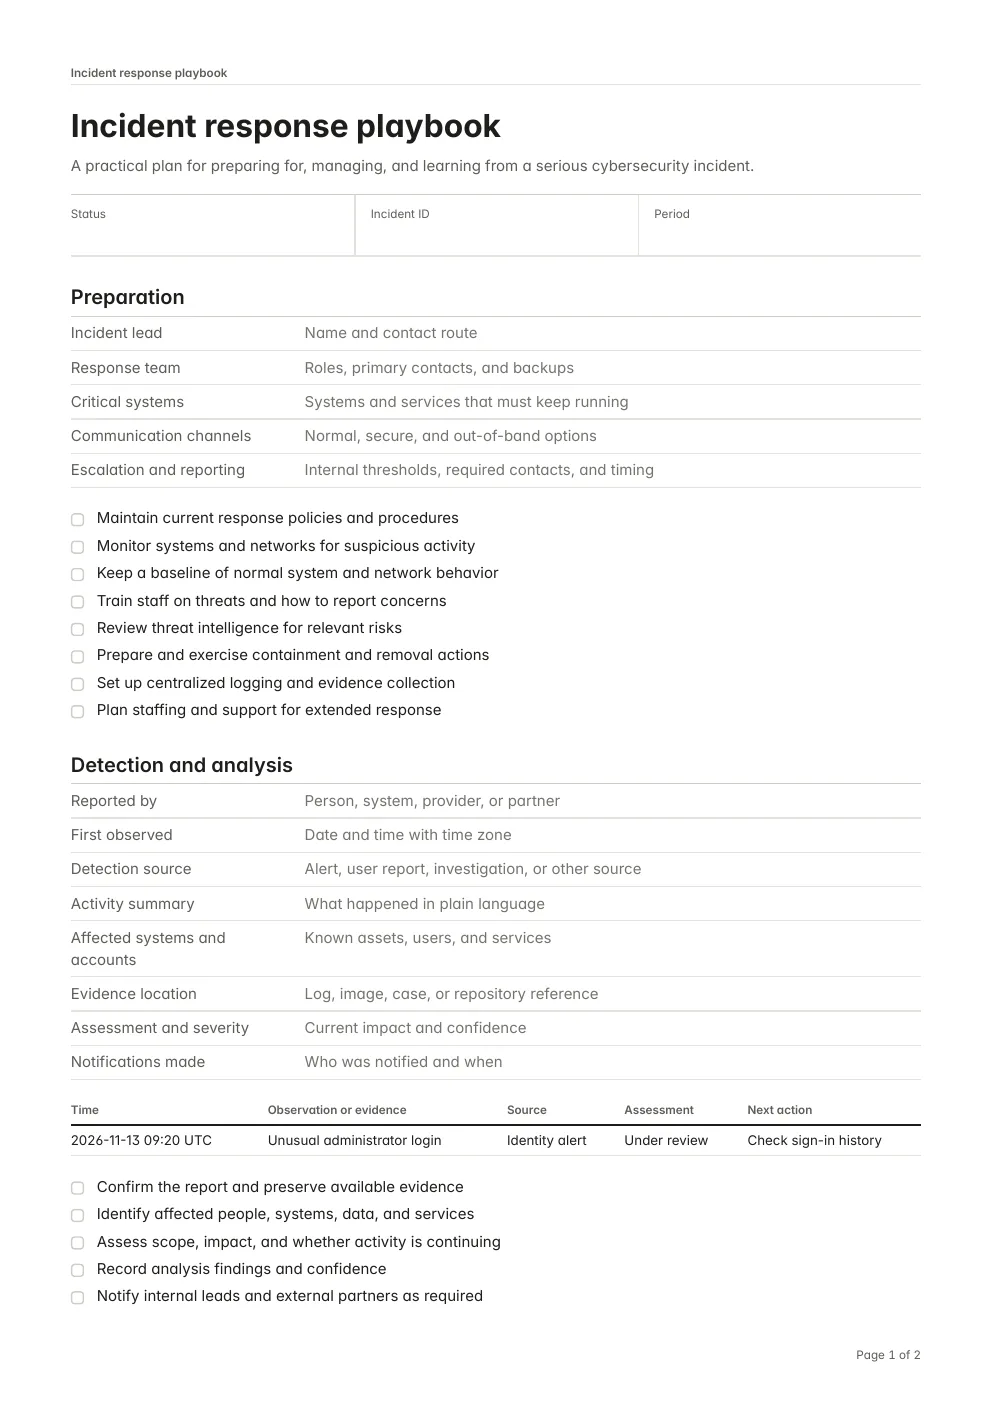
A practical plan for preparing for, managing, and learning from a serious cybersecurity incident. Use when malicious activity is confirmed or a serious incident has not yet been ruled out.
PreparationRecord the people, systems, procedures, and evidence paths needed before an incident.
Detection and analysisCapture how the activity was found, what is affected, and what evidence supports the assessment.
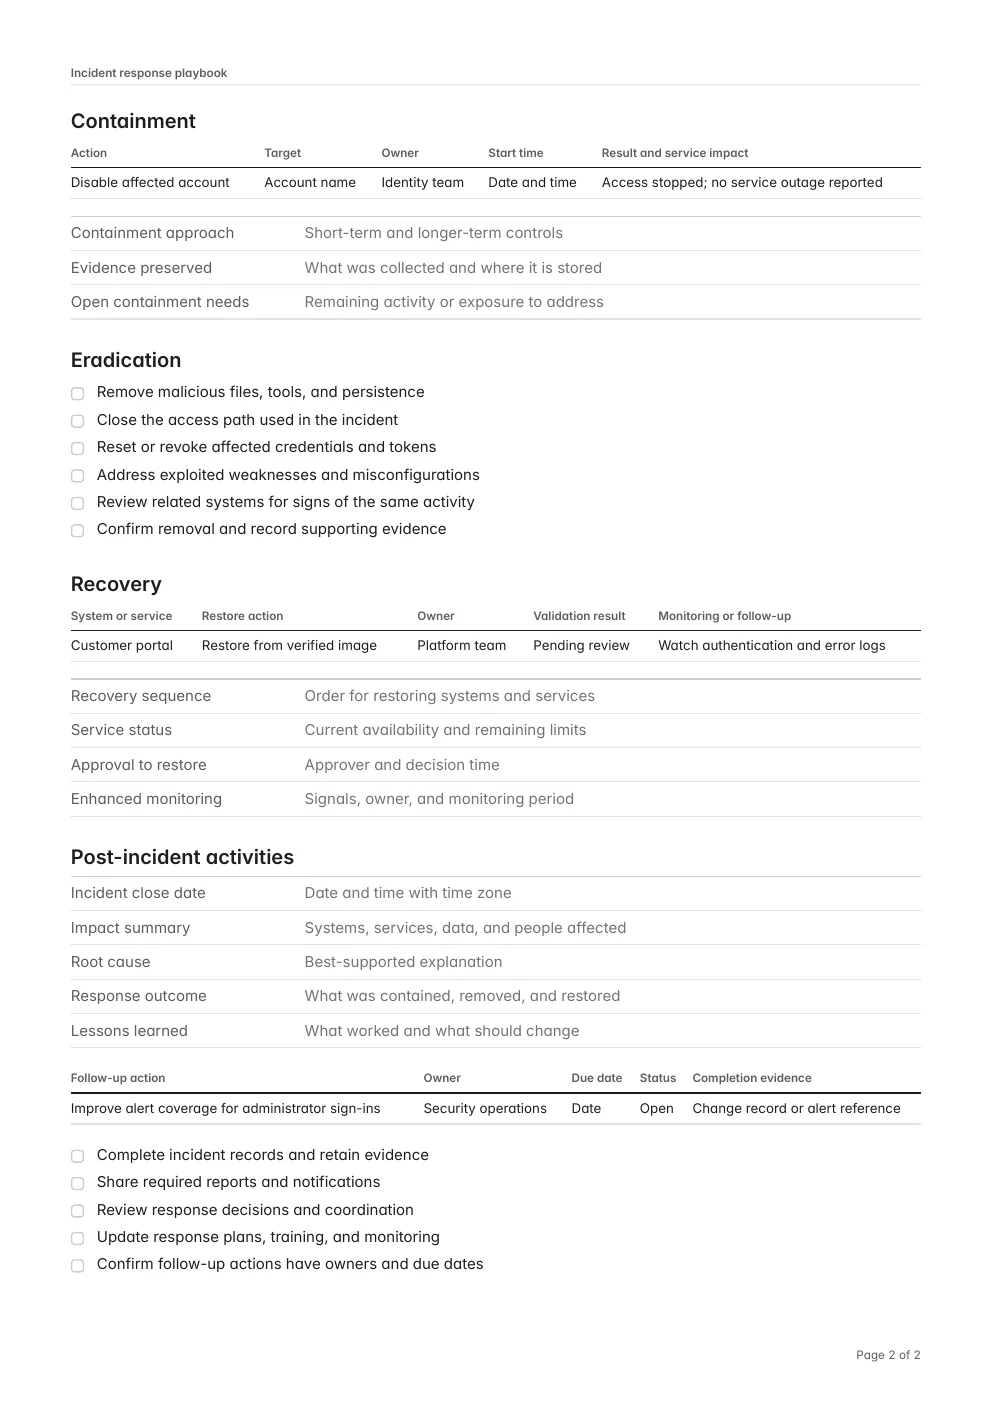
ContainmentDocument actions that limit spread or harm while preserving evidence and essential services.
EradicationRecord how the cause and any remaining malicious access will be removed.
RecoveryTrack the safe return of systems and services to normal operation.
Post-incident activitiesCapture the incident outcome, remaining work, and lessons that will improve future response.